30 Dec 2025 · Tiger3080 · 7 min read
Table of contents
- My complete learning journey with Altered Security’s most advanced Azure course
- Certified by Altered Security Red Team Expert for Azure (CARTE)
- My Experience With the Course Package
- Meet the New Instructor
- My Experience With the CARTE Course
- CARTE vs CARTP
- CARTE Exam Experience and Preparation
- My Preparation Strategy
- Exam Timeline and Experience
My complete learning journey with Altered Security’s most advanced Azure course
Certified by Altered Security Red Team Expert for Azure (CARTE)
I finally got the time to write a review of CARTE by Altered Security, and honestly, I’m very happy that I chose this path. Looking back, taking CARTE is easily one of the top 3 decisions in my learning journey, and I have absolutely no regrets.
The course is extremely well designed for anyone who truly wants to master Azure, not just learn cloud services at a surface level. CARTE helped me see Azure from a completely new perspective, especially how different services interact, where trust exists, and how attackers can abuse that trust when weaknesses appear.
What I appreciate most is that CARTE is not only about misconfigurations. Misconfigs are just one small part of real world attacks. The course goes much deeper by showing how some Azure features can be risky by default or vulnerable by design, depending on how Microsoft implements them and how organizations use them.
My Experience With the Course Package
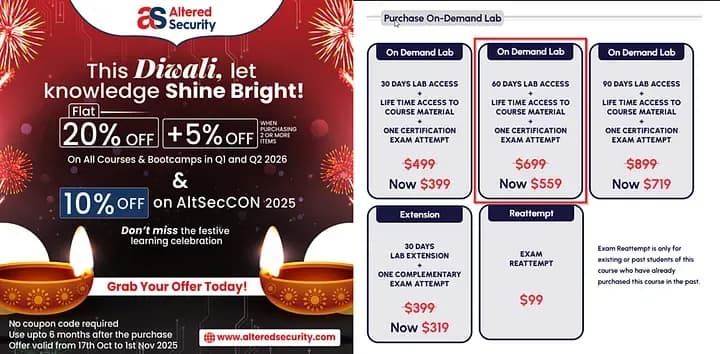
I bought this course during Diwali and received a 20% discount. Since I live in Thailand, this was my first time hearing about Diwali, which I learned is an important Indian festival associated with light, celebration, and new beginnings.
I chose the 60-day lab access package for $559 to be safe, and it turned out to be more than enough. I completed the entire course, all labs, and required notes in about one month plus an additional week, without needing the full access period.
During that time, I studied around 4 to 5 hours almost every day. Based on my experience, I would still recommend the 60-day package. Even if you can only study 2 to 3 hours per day and not every day, 60 days should be more than enough at a relaxed pace.
Meet the New Instructor
For CARTP and CRTP, I previously studied by following Nikhil’s course videos. This time, the course gives you the option to choose between two instructors. You can still learn through Nikhil’s videos by selecting the old course videos, or switch to the new course videos taught by Keanu.
So I decided to give Keanu a try. For me, he explained the topics very clearly and taught them really well. He covered everything in detail, included practical examples, and demonstrated how to perform the actions from the Azure portal, as well as how to prevent them. If there were alternative approaches in the lab, he explained those as well.
The best part for me was that I could understand his accent more clearly compared to Nikhil’s Indian accent. That made the learning process much easier for me and really helped throughout the course.
My Experience With the CARTE Course
This course introduced several new services that I had not used before, such as Privileged Identity Management (PIM), Temporary Access Pass (TAP), and Azure Lighthouse. The course goes beyond simply abusing misconfigurations. It also explains how these services can be abused due to weaknesses in their implementation, as well as how they can be properly secured.
One of my favorite topics, and one that I found especially interesting, was MFA bypass techniques. The explanations were clear and practical, which made the topic much easier to understand.
The course also covers initial access techniques, such as phishing, and introduces some interesting attack methods, including Device Code Phishing. I won’t go into detail about every topic covered here, but you can find the full course outline on the official website: https://www.alteredsecurity.com/carte
When you purchase the course, you also get access to the tools used throughout the labs. Some of these tools include deployment scripts. While they may require minor modifications before use, they are still very useful and provide a good foundation for real-world scenarios.
Another aspect I really liked about this course is the Kill Chain structure. When I studied CARTP, the course often jumped between different stages of the Kill Chain, which made it difficult to track where I was in the attack flow. In this course, each Kill Chain is covered one at a time, allowing you to fully complete one before moving on to the next. This made the learning process much clearer and easier to follow.
Finally, the lab support from Altered Security deserves special mention. I encountered a lab issue during my studies and contacted their support team by email. They resolved the issue in about 8 hours, which I found very fast. I emailed them late at night around 3 a.m., and they replied and fixed the issue by 10 a.m., which is especially impressive considering this happened on a Sunday.
CARTE vs CARTP
For me, the main difference between CARTE and CARTP is their focus. CARTP emphasizes enumeration and the fundamentals of Azure, helping you understand how Azure resources work together. CARTE, on the other hand, focuses on abuse techniques. It goes beyond simple misconfigurations and explores how Azure and Microsoft services can be abused, even within normal Microsoft workflows.
If you are unsure which course to choose, I strongly recommend starting with CARTP to build a solid foundation, and then moving on to CARTE. However, if you are already familiar with Azure, understand how its services work, and are comfortable with enumeration, you could skip CARTP and go directly to CARTE.
In my experience, CARTP is much easier and more straightforward, while CARTE is more advanced and assumes a stronger baseline knowledge.
CARTE Exam Experience and Preparation
The CARTE exam follows a 49/48-hour format. You are given 48 hours to complete the lab exam, plus an additional 1 hour for lab setup. In practice, the lab usually takes only about 10 to 15 minutes to start, but the extra hour provides a safety buffer. After completing the lab, you are given another 48 hours to submit the report. In total, this gives you roughly 97 hours to complete both the lab and the report.
My Preparation Strategy
My preparation was fairly simple and focused on the following points:
- Make sure your cheat sheet commands are well organized and ready to copy and use quickly.
- Ensure you fully understand the commands and the topics taught in the course, not just how to run them.
- Prepare a report template in advance to reduce time pressure during the exam.
- For me, I didn’t use any external tools or resources. Everything taught in the course was more than enough.
- Carefully read all exam notes before and during the exam. This is extremely important and very useful.
Exam Timeline and Experience
I started the exam on Friday at 1 p.m. and finished it on Monday at 1 a.m. To be clear, the exam does not require any brute-force attacks.
For me, the exam was quite straightforward at first. I reached about halfway within the first 4 hours, but then I got stuck for almost 20 hours (including sleep). Once I identified what I had missed, I was able to complete the remaining part of the exam in about 3 hours, for a total of roughly 27 hours spent on the lab.
Looking back, I could have finished earlier, but I didn’t enumerate thoroughly enough and missed a small but critical piece of information. I found all the other parts, but missing that one detail cost me a lot of time. During that period, I was very frustrated and genuinely thought I might fail the exam.
Once I discovered the missing piece, everything became much easier. I had already identified all the possible paths, and that single missing detail was the only thing blocking my progress.
Overall, the exam was fun, challenging, and well designed by Altered Security. It truly tests whether students understand what they are doing, rather than just following steps blindly.
For the remaining lab time, I focused on capturing evidence and command output for the report. I then completed the report well within the 48-hour reporting window, finishing it in under 24 hours, as I needed to return to work the next day.
Now I am a Certified by Altered Security Red Team Expert for Azure.